Related Topics:
Core Access Switche-
Core switches support routing functionality
Core Switches support various routing protocols, such as OSPF (Open Shortest Path First) and BGP (Border Gateway Protocol), enabling intelligent selection of optimal paths for data forwarding based on routing tables. A Core Switch is a high-performance network switch designed to handle large amounts of data traffic, typically positioned at the center of a network, connecting different subnets, VLANs (Virtual Local Area Networks), or network areas. The devices like high-capacity transmitters are placed in this layer. The core. on Cisco Learning Zone E-Learning Series initiative. The Learning Zone is a complete program of training from Cisco IT, aiming to empower employees, at a number of pro re Routing and Switching within Cisco Systems today. This module aims to outline an executive overview of the deployment, the ben n.
[PDF Version]
-
Huawei Core Switch Optical Port Aggregation
CloudEngine S6750-H series 10GE switches are Huawei's next-generation enterprise-class switches designed for core and aggregation layers, with 48 × 10GE downlink optical ports and 8 × 100GE uplink optical ports. They feature high performance, high reliability, cloud management, and intelligent O&M. Attacks to networks refer to STP BPDU/root attacks. Attacks to users include bogus DHCP server attacks, man-in-the-middle attacks, IP/MAC spoofing attacks, and DHCP request flood attacks. DoS attacks that change the CHADDR field in DHCP packets are also attacks against users. Device installation. This document describes the configuration of Ethernet services, including configuring link aggregation, VLANs, Voice VLAN, VLAN mapping, QinQ, GVRP, MAC table, STP/RSTP/MSTP, SEP, and so on.
[PDF Version]
-
Switch Access Security Configuration
Use Strong Passwords: Configure strong, unique passwords for all switch accounts, avoiding default or weak credentials. Enable SSH: Disable insecure protocols like Telnet and enable Secure Shell (SSH) for remote management. Convoluted type 9 secret is supported in Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device. Before you downgrade to any. Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access. Control Plane: Control plane consists of the protocols and processes that. Configuring a local Manager password is a fundamental step in reducing the possibility of unauthorized access through the switch WebAgent and console (CLI and Menu) interfaces. Access Security provides different security measures for accessing the switch remotely so as to enhance the configuration management security. This function is used to control the users' access to the switch based on IP address, MAC address or port.
[PDF Version]
-
4 PoE switches connected to the core switch
In a star topology, all PoE switches are connected directly to a core switch, forming a central hub, which allows for efficient data transfer and power distribution. There are different types of enterprise switches that perform various roles in these layer-based or hierarchical ethernet networks. This white paper introduces the. A PoE switch is a network switch that utilizes PoE technology to transmit power and data over the same Ethernet cable to powered devices such as IP cameras, wireless access points, and VoIP phones, simplifying installation and reducing maintenance costs. Is there a specific process that I should be using to link these switches together ? Should I use specific ports or configure a setting within each switch ? Generally your highest density switch, in this case. It is a powerful backbone switch in the center of the network core layer, which centralizes multiple aggregation switches to the core and implements LAN routing.
[PDF Version]
-
Frequent up down of access switch interfaces
You can use the following commands on CLI to check the status of the interfaces. The Output log lines will show the change of the interface status and help to find if the interface was frequently up and down or not: grep -E "Link. *is (DOWN|UP)" /var/log/ltm* | sed -r 's/^ :]+://g' | . The same port is going up and down many times and it is not about one switch or one user. There are no specific requirements for this document. This document applies to Catalyst switches that run on Cisco IOS® System Software. Is this a normal thing? Should I be troubleshooting layer 1? 3650: Hardware is Gigabit Ethernet, address is 0027. All phones a part of voice VLAN Strangely, when we connect. I am a novice with Cisco switches – I have a switch with some ports that keep oscillating between up and down: Here are the settings on port 1/0/22: How do I diagnose this problem? Post a “show interface fastEthernet 1/0/22” from CLI, or screen from Cisco Network Assistant (interface status, errors.
[PDF Version]
-
Security Configuration of Core Switch Ports
This complete port security configuration guide covers sticky MAC address learning, violation modes, troubleshooting err-disabled ports, and advanced security scenarios that networking professionals use daily. If you try to set the maximum value to a number less than the number of secure addresses already configured on an interface, the command is rejected. To understand port security, you should be familiar with how switches learn MAC addresses. Let's. To block unauthorized access to switch ports, switches support a feature called port security. This tutorial explains. In MAC-flooding, an attacker can connect a laptop into an empty Switch port or empty RJ45 wall socket, and he can use hacking tools to generate millions of Ethernet frames with fake source MAC addresses and send them to the switch interface.
[PDF Version]
-
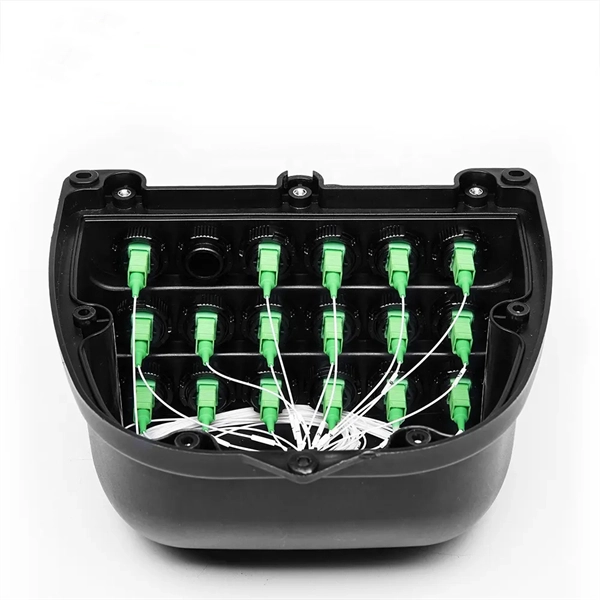
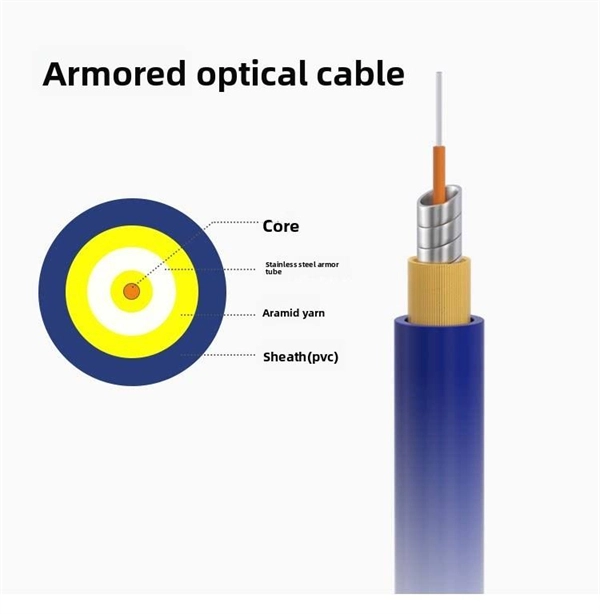
Fiber optic backup clamps can protect the fiber optic cable core
A fiber clamp is designed to hold and protect fiber optic cables securely in place during installation and throughout their operational life. These clamps provide a secure foundation for the cables, helping to prevent damage and maintain proper alignment and. These cable management products offer a choice of methods to secure, route, label, and bundle electrical cables and fiber optic patch cables. 1 to quickly navigate the page. They transmit data at incredibly high speeds over long distances by using light signals.