Related Topics:
Port Security Cisco Explained-
Huawei Core Switch Optical Port Aggregation
CloudEngine S6750-H series 10GE switches are Huawei's next-generation enterprise-class switches designed for core and aggregation layers, with 48 × 10GE downlink optical ports and 8 × 100GE uplink optical ports. They feature high performance, high reliability, cloud management, and intelligent O&M. Attacks to networks refer to STP BPDU/root attacks. Attacks to users include bogus DHCP server attacks, man-in-the-middle attacks, IP/MAC spoofing attacks, and DHCP request flood attacks. DoS attacks that change the CHADDR field in DHCP packets are also attacks against users. Device installation. This document describes the configuration of Ethernet services, including configuring link aggregation, VLANs, Voice VLAN, VLAN mapping, QinQ, GVRP, MAC table, STP/RSTP/MSTP, SEP, and so on.
[PDF Version]
-
What color is the optical port LED on the switch
One bicolor (green/amber) port status LED for each port on the switch. These LEDs are located above each pair of Fibre Channel ports. Each Ethernet port, 1-Gigabit Ethernet module slot, and 10-Gigabit Ethernet module slot has a port LED. The port status LEDs for the FC ports are arranged left and. The LED colors for the switch and their corresponding status indications are as follows ; To Select or change a mode, press the mode button until the desired mode is highlighted.
-
Switch Access Security Configuration
Use Strong Passwords: Configure strong, unique passwords for all switch accounts, avoiding default or weak credentials. Enable SSH: Disable insecure protocols like Telnet and enable Secure Shell (SSH) for remote management. Convoluted type 9 secret is supported in Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device. Before you downgrade to any. Cisco Meraki MS switches offer the ability to configure access policies, which require connecting devices to authenticate against a RADIUS server before they are granted network access. Control Plane: Control plane consists of the protocols and processes that. Configuring a local Manager password is a fundamental step in reducing the possibility of unauthorized access through the switch WebAgent and console (CLI and Menu) interfaces. Access Security provides different security measures for accessing the switch remotely so as to enhance the configuration management security. This function is used to control the users' access to the switch based on IP address, MAC address or port.
[PDF Version]
-
400G Optical Module for Security and Remote Monitoring
Cisco 400G QSFP-DD High-Power (Bright) Optical module's small size and low power make it an optimal choice for a wide range of DCI/Cloud, metro access/aggregation, wireless backhaul, and campus interconnect applications. First, let's clarify what VR, SR, DR, FR, LR, ER, and ZR stand for, so that we can understand and identify them: VR (Very Short Range): Transmission distance usually 0~100 meters, using multimode fiber for short data center connections. This article explores the enabling technologies, performance. Cisco is now expanding the range of 400G Digital Coherent QSFP-DD transceivers, introducing High Tx Power variants (+1dBm of Tx Power). The electrical signal is converted into an optical signal at the transmitter, which then travels through fiber optics, and is converted back to an electrical signal at the receiver. It is primarily applied in data center interconnect (DCI), AI clusters, large-scale cloud networks, and telecom backbones. Taking the QSFP-DD package as an example, its working principle is shown in the figure below.
[PDF Version]
-
Network security devices in daily life
This blog explores essential networking devices, including firewalls, IDS/IPS, VPNs, NAC, SIEM, WAFs, and network analyzers, explaining their real-time applications and importance in preventing cyberattacks. Network security involves tools, techniques, and policies to protect digital assets from unauthorized access and cyber threats. A key strategy in network security is the multi-layered defense. This article delves into the multifaceted uses of network security in daily life, demonstrating how it underpins our actions and decisions, fortifies our data, and shapes our interactions with technology. The first and most immediate application of network security can be seen in personal safety.
-
Which port is best for the optical splitter
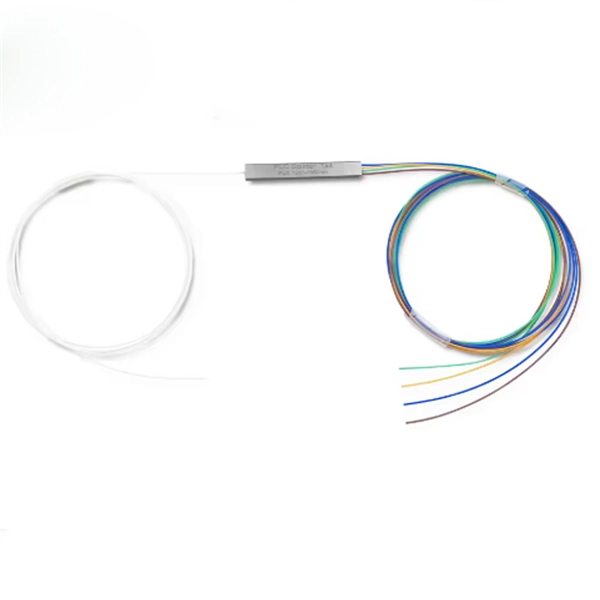
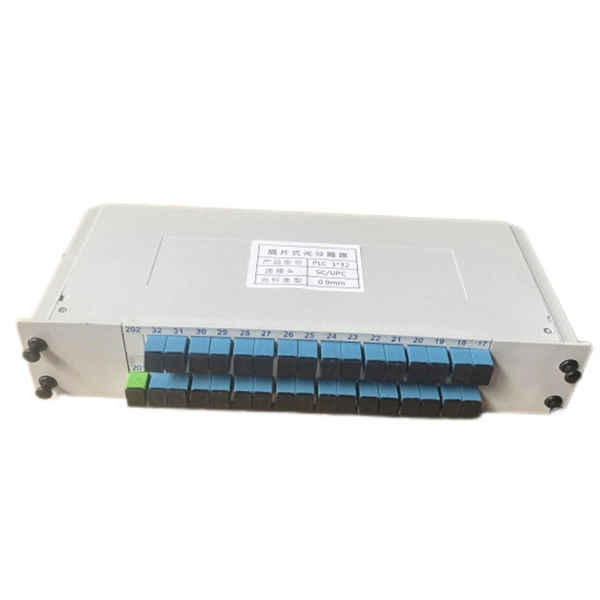
It is generally used in the optical line terminal OLT and the optical network terminal ONU of the passive optical network to realize the optical signal splitting. According to the Broadband Forum, PLC splitters are essential for achieving scalable and cost-effective GPON and XGS-PON deployment in access networks. In this guide, you'll learn how fiber splitters function in PON networks, the difference between PLC and FBT types, and how to choose the best. A fiber broadband provider typically determines and overall split ratio for the network, such as 1x32 or 1x64, and uses combinations of splitters to meet that ratio with each PON port. 1x32 splits were common in North America for G-PON architectures. Unlike active devices (which require power), splitters operate without electricity, relying solely on the physics of. According to Lightwave Online, FTTH growth is accelerating demand for high-performance passive fiber splitters worldwide.
[PDF Version]
-
How to use a cable TV splitter to an Ethernet port
Plug your router's main Ethernet cable into the Dockteck splitter's input port. The splitter uses USB power to maintain a stable signal transmission, ensuring a stable data flow even when multiple devices are in. An Ethernet splitter, also known as a network splitter or LAN splitter, is a device designed to divide one Ethernet connection into multiple outputs. This effectively turns one cable into two, and it can be a useful way to double the number of devices you can connect to a single cable.